DPO or not to DPO: The Data Protection Officer under GDPR

clip_image002

The General Data Protection Regulation (GDPR) is nearly upon us and one of the elements is the requirement for certain organisations to have a Data Protection Officer.

This throws up some interesting issues. A qualified, experienced data protection officer is a valuable commodity. They do exist but command salaries approaching £50,000 in large organisations (stop laughing at the back) and if you’re a small organisation they’re not going to work for you for peanuts. So where do you find a qualified, experienced DPO?

Secondly will there be a requirement upon you to have one? It looks like there will be three clear cases.

  1. processing is carried out by a public authority,
  2. the core activities of the controller or processor consist of processing which, by its nature, scope or purposes, requires regular and systematic monitoring
    of data subjects on a large scale
  3. the core activities consist of processing on a large scale of special categories of data.

But to go back to the DPO what does qualified mean? Yes there are qualifications out there. The accepted gold standard in the UK is the BCS certificate which has 40 hours of training plus a testing 3 hour exam. There are other firms in the sector who offer their own versions and most of them involve significant study (30 or 40 hours) plus exam. Other qualifications exist, like our GDPR Practitioner Certificate and CIPP certification from the International Association of Privacy Professionals – some for US and some for UK professionals – but the question everyone wants answering is which qualifications will satisfy the GDPR?

Do training providers have to apply for acceptance or endorsement from the EU or their national regulator? Will the content of these courses be examined or will a standard be set and the training providers tailor their material to a certain level or will it be a free for all with no standard to work to? Do you want a DPO who knows how to conduct a Privacy Impact Assessment or who knows about International Data Transfers or one with an understanding of the history of Data Protection? Or will there be a requirement to study a certain (large) number of hours to demonstrate competence? At the moment it looks like all the DPO will need is “sufficient expert knowledge” which doesn’t in itself mean a qualification.

Other skills required by a good DPO are those of Diplomat, Trainer; Advisor, Confidante; Interpreter; Persuader; Listener; Friend to requestors; Policy & procedures writer. They have the ability to talk to the top level of the organisation yet explain complex law in Plain English. Not your run of the mill person.

It looks like the route map will require the DPO to be an employee but one with a different type of outlook. Privacy is becoming a big vote winner; organisations who don’t respect customers privacy will feel the backlash of disgruntled consumers. It really needs someone who is part of the organisation who is present at all times and understand the data processing systems of their employer but is detached enough to be able to criticize his own organisation.

There is a way out for small organisations who think they need a DPO to ensure their organisation is fully compliant with the new regulation. Don’t give the job to an existing member of staff and expect them to learn it on the job; Don’t appoint a knowledgeable, qualified, experienced but expensive DPO – bring in an external one you can use as and when you need them.

Externals have significant benefits. They don’t work full time so the on costs disappear; You can bring them in as required for short term task and finish assignments; You can save the costs of training and continuing education for an internal data protection officer; your staff will react better to an external who appears to have the status of a “consultant”.

Externals also won’t have any political or organisational baggage and can act in an unbiased manner without fear for their job. An external data protection officer also has no worries about favouring certain departments or individuals in the company. Many organisations appoint their Head of Legal as their DPO which brings with it the ethical/legal/best course of action conflict. An external won’t need to bother with this.

You can concentrate on your core business and the external can take care of your data protection.

Once you have appointed an external DPO they will compile a detailed data protection audit on your data protection compliance. They will then identify possible data protection issues and legal risks and explain what is required to remedy them. Then you can start making the necessary changes.  Your business will soon be in full compliance with current data protection laws.

But it doesn’t stop there. The external DPO will be on call and can discuss day-to-day DP issues by phone or email for a small fee. If more detailed work is required further fees and timescales can be agreed.

Working with an external data protection officer is based on a consulting agreement. There may be a retainer fee plus an hourly or daily rate to follow. If your Data Protection needs are low you may not have to consult your EDPO too often.

Not surprisingly EDPOs are starting to appear on the web. They’re quite common in Germany and it’s likely they will become a staple in the UK. Various UK law firms advertise such a service but unsurprisingly the rates they charge are not on view. It might end up costing more than you think especially if you opt for a ’big’ name.

There’s also the scope however for sharing a DPO. This has already happened in various parts of the country as cash strapped rural councils pay for a percentage of a DPO and have them on site part of a week.

At a recent educational conference a group of 30 schools in the same region kicked around the idea of each contributing to buy a DPO for all of them who would fulfill their information law obligations. Sounds quite a good idea until you realise there’s only about 240 working days in a year so each school would have 8 of those days to themselves and the shared DPO would have a significant petrol expenses tab. A few rural councils with a shared DPO would have a much better deal.

Sadly GDPR is not well understood and there are those who think Brexit will derail it (though not true) but a wise organisation should be thinking now if and when they will need a DPO, what qualification they will have and how do they find one.

An external who is called on infrequently might appear be the cheapest option but might have further hidden costs and a part share of a DPO might be a good short term solution but would they be as good as the expert knowledge and day to day hands on work of a full timer.

Good news for Data Protection Officers…

We are running a series of GDPR webinars and workshops and our team of experts are available to come to your organisation to deliver customised data protection/GDPR workshops as well as to carry out health checks and audits. Our GDPR Practitioner Certificate (GDPR.Cert), with an emphasis on the practical skills required to implement GDPR, is an ideal qualification for those aspiring for such positions.

Act Now DP Practitioner Certificate: Latest Results

2016dpp-page-001

Act Now Training’s Data Protection Practitioner Certificate continues to go from strength to strength. The two remaining courses in 2016 are fully booked and the latest set of results and delegate feedback show that it is an ideal qualification for those who work with Data Protection and privacy issues on a day-to-day basis.

In September 2016, a total of 14 delegates passed the course of which 10 achieved a distinction. As ever there was a wide range of delegates from the local government, health, education and private sectors.

Candidates were delighted with their results. They really appreciated the effort put in by our expert speaker Tim Turner:

“The course really was excellent and I would thoroughly recommend it. Data Protection can be a dry subject, but not when delivered by Tim – he kept my full attention from beginning to end with his excellent and interesting presentation, and invaluable advice.”  SB, Lancashire CC

“Tim broke the course down into manageable chunks and gave useful, practical examples that illustrated his points. This course has given me not only the knowledge but also the confidence to improve at my job and make my organisation better too!” DH, Cheshire West and Chester Council

“Tim imparts a huge amount of information in an accessible, user-friendly way that has never felt overwhelming.” SM, University of Surrey

The emphasis of the course is on practical skills which a Data protection Officers need to do their job and raise DP standards in their organisation. This is something, which was emphasised by our delegates in their feedback:

“I would thoroughly recommend the course, which has a sensible, practical focus and deals with the application of an otherwise abstract and complex piece of legislation to real life situations.”  AG, Parliamentary and Health Service Ombudsman

“The course provided useful practical examples which makes it easy to apply the DPA and identify a potential breach in a scenario – Immensely useful :).” BA, Nursing and Midwifery Council

“Great, thorough presentation and discussion of the practical implementations of data protection, the Act and its future developments.” PC, University of the Highlands and Islands

The course syllabus continues to be revised to include more themes covered by the General Data Protection Regulation (GDPR) which will come in force in May 2018  (and which is still relevant despite the Brexit vote).

The course, designed in consultation with a panel of experts from the UK and Europe, takes place over four days (one day per week) and involves lectures, assessments and exercises. This is followed by a written assessment. Candidates are then required to complete a practical project (in their own time) to achieve the certificate.

If you don’t have the time to attend for four consecutive weeks, why not try our intensive course in Summer 2017?

To learn more please visit our website or get in touch.

GDPR Practitioner Certificate (GDPR.Cert) – A 4 day certificated course aimed at those undertaking the role of Data Protection Officer under GDPR whether in the public or the private sector. It builds on the success of the Act Now Data Protection Practitioner Certificate (launched in April 2014), which it replaces, by focussing on GDPR.

IG Dates for your Diary – Let’s seize the day(s)!

canstockphoto15551787-1


By Frank Rankin

It always seems to be the national or international day of something-or-other.  As I write it is (as decreed by the United Nations) International Democracy Day. Coming soon we will have (as decreed by a couple of strange blokes in Oregon) International Talk Like A Pirate Day.

As well as providing useful space-fillers to lazy journalists on slow news days, such commemorations are often used to draw attention to serious (or silly) issues.

And as information governance practitioners, why should we miss out?

There are a few calendar dates which we can possibly exploit in the never-ending task of raising awareness among our managers and co-workers of some of the key messages around FOI, data protection and information security.

I plan to send some communications to my colleagues in the NHS organisation where I work, commemorating International Right to Know Day on 28 September. Initiated by FOI activists from around the world in 2002, the day seeks to celebrate successes in improving government transparency, and highlighting continuing struggles. It provides an excuse for me to gently remind colleagues that they could be the recipient of FOI requests and how they should react. I’ll also remind them of the rights that they have as citizens. (Why not put up some FOI posters Frank? Ed.)

October is National Cyber Security Awareness Month and 7 February 2017 will be Safer Internet Day. In drawing the attention of colleagues to guidance and resources to help them keep their families safe online, we also build their skills and awareness to improve security in the workplace. On the last Safer Internet Day we took the opportunity to send tips to colleagues on how to protect themselves and their children from phishing, malware and other nasties. It is the first time I have ever received notes of thanks for an information governance awareness programme!

Across Europe, Data Protection Day is marked on 28 January – the anniversary of the signing of the Council of Europe’s Convention 108 for the Protection of individuals with regard to automatic processing of personal data, ancestor to the forthcoming General Data Protection Regulation (GDPR). Although I am sure you all knew that.  (Well, Tim Turner probably did.)  (Dear reader, it is still relevant despite the Brexit vote.Ed)

While I don’t expect to see MoonPig selling cards for the occasion, again it gives us a hook to hang an awareness message on – perhaps some reminders of appropriate behaviours we expect from staff to protect the personal data we hold, as well as an update on GDPR developments. (Er why not put up some GDPR posters Frank?Ed.)

But Frank, I hear some of you object, aren’t these commemorative dates just a wee bit cheesy? Perhaps. But I am not too proud to borrow any excuse to highlight information governance messages in a way that reminds our people that these issues are universal.

Back in the 1990s, the late Declan Treacy used to champion International Clear Your Desk Day as an opportunity to declutter our work spaces, delivering benefits for ergonomics, mental health and feng shui – as well as for records management and data security. Alas, no-one seems to have picked up the mantle since his death.

So, who is with me? Let’s pick a date and I’ll see you at the confidential waste bin.

Frank Rankin is an information security, FOI and records management expert. Amongst other courses he is currently delivering our Practitioner Certificate in Freedom of Information (Scotland).

Privacy Notices under #GDPR: Have you noticed my notice?

DPA2Please also read our updated blog on privacy notices here.

As you all know by now the General Data Protection Regulation (GDPR) is here and it is (as predicted) starting to get various people fired up ready for its 2018 implementation date. (Dear reader, it is still relevant despite the Brexit vote.) We’ve been exploring various aspects of the GDPR and in this particular blog I want us to look at the concept of privacy notices and what they will need to start looking like under the Regulation.

Data Protection Act 1998:

Under the current Data Protection Act 1998, and indeed the Information Commissioner’s Office Privacy Notices Code of Practice, privacy notices should be on any collection point where personal data is being collected from a Data Subject. Especially if being collected for a new purpose. In that notice Data Controllers should (at the very least) include the following;

  • The identity of the Organisation in control of the processing;
  • The purpose, or purposes, for which the information will be processed;
  • Any further information necessary, in the specific circumstances, to enable the processing in respect of the individual to be ‘fair’ (in accordance with the 1st Principle).

The requirements also outline that this information must be clear and in ‘plain English’ and your purposes cannot be too vague. The less vague the purpose the less likely it’s going to be a valid consent (or indeed a valid notification if you are not relying on consent).

While privacy notices vary most of them aren’t that much longer than your average paragraph (the paragraph I’ve just written for example) and that, providing it’s clear, concise and meets your legal grounds for processing, is generally how privacy notices work under the Data Protection Act 1998. Further information on a Controllers processing is then often outlined in Terms and Conditions either in the contract paperwork or online.

The New World:

The GDPR builds on the current expectations around privacy notices but expands on the requirements based on the widened first principle which now specifically requires controllers to be transparent with their processing.

Article 13 Paragraph 1 (a-f) of the GDPR outlines that the following information should be provided to the data subject at the point of data collection;

(a) the identity and the contact details of the controller and, where applicable, of the controller’s representative;

(b) the contact details of the data protection officer, where applicable;

(c) the purposes of the processing for which the personal data are intended as well as the legal basis for the processing;

(d) where the processing is based on point (f) of Article 6(1), the legitimate interests pursued by the controller or by a third party;

(e) the recipients or categories of recipients of the personal data, if any;

(f) where applicable, the fact that the controller intends to transfer personal data to a third country or international organisation and the existence or absence of an adequacy decision by the Commission, or in the case of transfers referred to in Article 46 or 47, or the second subparagraph of Article 49(1), reference to the appropriate or suitable safeguards and the means by which to obtain a copy of them or where they have been made available.

Depending on what processing is going on, Article 13 Paragraph 2 (a-f) states that controllers will also need to provide some of the following;

(a) the period for which the personal data will be stored, or if that is not possible, the criteria used to determine that period;

(b) the existence of the right to request from the controller access to and rectification or erasure of personal data or restriction of processing concerning the data subject or to object to processing as well as the right to data portability;

(c) where the processing is based on point (a) of Article 6(1) or point (a) of Article 9(2), the existence of the right to withdraw consent at any time, without affecting the lawfulness of processing based on consent before its withdrawal;

(d) the right to lodge a complaint with a supervisory authority;

(e) whether the provision of personal data is a statutory or contractual requirement, or a requirement necessary to enter into a contract, as well as whether the data subject is obliged to provide the personal data and of the possible consequences of failure to provide such data;

(f) the existence of automated decision-making, including profiling, referred to in Article 22(1) and (4) and, at least in those cases, meaningful information about the logic involved, as well as the significance and the envisaged consequences of such processing for the data subject.

Now if you are engaging in some quite complicated processing, like in the insurance industry for example, your new notices under GDPR are going to need to strike a balance between being ‘too much information’ and being far too simple and high level that they don’t actually meet your transparency requirements to demonstrate effective notice or consent.

Article 13 Paragraph 3 also outlines that should a controller seek to process personal data for purposes different to which it was collected the controller shall project the subject (prior to that processing commencing) information on that purpose and any other relevant information from paragraph 2.

I’ve attempted to ‘mock up’ what one of these new notices could look like. Now this is very much an imaginary one but if we assume that a controller is processing Personal Data for complex purposes their notice may look something like this;

Your Personal Data:

What we need

The A Notice Ltd will be what’s known as the ‘Controller’ of the personal data you provide to us. We only collect basic personal data about you which does not include any special types of information or location based information. This does however include name, address, email etc.

Why we need it

We need to know your basic personal data in order to provide you with notice writing and analysis services in line with this overall contract. We will not collect any personal data from you we do not need in order to provide and oversee this service to you.

What we do with it

All the personal data we process is processed by our staff in the UK however for the purposes of IT hosting and maintenance this information is located on servers within the European Union. No 3rd parties have access to your personal data unless the law allows them to do so.

We have a Data Protection regime in place to oversee the effective and secure processing of your personal data. More information on this framework can be found on our website.

How long we keep it

We are required under UK tax law to keep your basic personal data (name, address, contact details) for a minimum of 6 years after which time it will be destroyed. Your information we use for marketing purposes will be kept with us until you notify us that you no longer wish to receive this information. More information on our retention schedule can be found online.

What we would also like to do with it

We would however like to use your name and email address to inform you of our future offers and similar products. This information is not shared with third purposes and you can unsubscribe at any time via phone, email or our website. Please indicate below if this is something you would like to sign up to.

Please sign me up to receive details about future offers from A Notice Ltd.

What are your rights?

If at any point you believe the information we process on you is incorrect you request to see this information and even have it corrected or deleted. If you wish to raise a complaint on how we have handled your personal data, you can contact our Data Protection Officer who will investigate the matter.

If you are not satisfied with our response or believe we are processing your personal data not in accordance with the law you can complain to the Information Commissioner’s Office (ICO).

Our Data Protection Officer is Notice McNoticeface and you can contact them at mypersonaldata@anotice.com.

This example is working on the assumption of a simple data processing arrangement. The more complex your data processing the more complex that notice and consent capture will need to be. But this must be comprehensible to the average consumer and cannot be a work of ‘legal-ee brilliance’ that makes no sense to those not trained in law.

I suspect that notices will allow ‘outlines of categories’ of types of processing and third parties however we shall see how big these categories can be. After all, the bigger the ‘bucket’ the less you are actually giving a robust ‘informed’ notice to a data subject.

In addition to all of this, Article 14 states that should you obtain Personal Data via a means not direct from the Data Subject themselves you also need to provide a notification to them (with some exceptions);

(a) within a reasonable period after obtaining the personal data, but at the latest within one month, having regard to the specific circumstances in which the personal data are processed;

(b) if the personal data are to be used for communication with the data subject, at the latest at the time of the first communication to that data subject; or

(c) if a disclosure to another recipient is envisaged, at the latest when the personal data are first disclosed.

The requirement is to provide them with very similar information that you would provide to them if you collected the data directly. How you do this will be a matter of some discussion to come but excluding the reasons outlined in Article 14 (5) (a – d), if you aren’t collecting directly you will now need to take steps to advise and ‘notify’ the Data Subject of what you are up to.

Now that is quite a long list of things to notify a data subject of, especially if you are delivering various services to the data subject (and collecting data on them) via various means. But Paragraph 4 does say that all of the above shall not apply if the data subject already has the data. So, for example, if a customer is simply renewing a service and nothing about the provision of that service (the processing) has changed then there is no obvious requirement here to re-issue the original notice at that point of renewal.

We will delve into the concept of consent at another time (very soon) but the requirement to be transparent as well as the requirement to ensure you have a clear and documented consent means that privacy notices are going to have to become more than just a long legal document but that far away from what we are doing today (assuming we are doing them correctly that is).

More on privacy notices here.

Scott Sammons CIPP/E, AMIRMS is an experienced Data Protection & Information Risk practitioner and a consultant with Act Now Training.

If you need to raise awareness about GDPR, our GDPR e learning course is ideal for frontline staff. Advice and guidance on GDPR is available through our GDPR helpline.

GDPR Practitioner Certificate – A 4 day certificated course aimed at those undertaking the role of Data Protection Officer under GDPR whether in the public or the private sector.

Data Protection Reform after Brexit. Does GDPR still matter?

gdprAccording to the new Prime Minister “Brexit means Brexit.” But what does Brexit mean for UK Data Controllers who are planning for implementation of the new General Data Protection Regulation (GDPR)? The short answer is keep calm and carry on.

GDPR received formal adoption by the European Parliament in April 2016 and was published on 4th May in the Official Journal. This means that it will be directly applicable throughout EU member states (without the need for implementing legislation) from 25th May 2018. Following the referendum result, you might be forgiven for thinking that you can shred your copy of the Regulation or indeed cancel your place on our very popular GDPR workshop.

The UK may have voted to leave the EU but formal divorce proceedings cannot begin until it notifies the EU of its intention to invoke Article 50 of the Lisbon Treaty. This gives negotiators two years from the date of notification to conclude new arrangements. The newly appointed Secretary of State for Exiting the European Union, David Davis, has said Article 50 should be “triggered before or by the beginning of next year.” Therefore the UK could leave the EU by December 2018 at the earliest. Consequently there would be at least six months where UK Data Controllers would have to abide by all the provisions of GDPR. In reality exiting the EU could take much longer than two years and so we could be stuck with GDPR for much longer.

In the unlikely event that Brexit negotiations are concluded before May 2018, the DPA is still living on borrowed time. Immediately after the Brexit vote the Information Commissioner’s Office (ICO), released a statement saying:

“If the UK wants to trade with the Single Market on equal terms we would have to prove ‘adequacy’—in other words UK data protection standards would have to be equivalent to the EU’s General Data Protection Regulation framework starting in 2018.”

In a speech on 4th July 2016 the then Minister for Data Protection, Baroness Neville-Rolfe, touched on the future of data protection: (HT Panopticon Blog)

“One thing we can say with reasonable confidence is that if any country wishes to share data with EU Member States, or for it to handle EU citizens’ data, they will need to be assessed as providing an adequate level of data protection. This will be a major consideration in the UK’s negotiations going forward….”

The law firm, Bird and Bird, have set out the options available to the UK in terms of exiting the EU and its implications for data protection. Each of these options makes it likely that either the GDPR or a very close cousin will be required in the UK after Brexit takes effect.

Regardless of what data protection path the UK chooses, UK companies with European customers and operations have to continue with preparations. This is because GDPR will apply to any entity offering goods or services (regardless of payment being taken) and any entity monitoring the behaviours of citizens residing within the EU. Companies will be directly responsible for GDPR compliance wherever they are based (and not just their EU based offices) as long as they are processing EU citizens’ personal data.

Recently on the ICO’s Blog,  the message was reiterated that GDPR is still relevant and preparation must continue:

“We’ve been working hard on producing a set of guidance on GDPR, with an overview of the law being the first substantive part of that. We still think it will be useful to publish this overview. This is because once implemented in the EU, the GDPR will be relevant for many organisations in the UK – most obviously those operating internationally. The other main reason is that the GDPR has several new features – for example breach notification and data portability. Therefore, we thought it would still be useful to familiarise information rights professionals with the GDPR’s main principles and concepts.”

 Data Controllers have two years to prepare for the biggest change to the EU data protection regime in 20 years.  Many provisions such as breach notification and the new DP Principles will require careful planning. With some GDPR breaches carrying fines of up to 4% of global annual turnover or 20 million Euros, a “wait and see” approach would be very risky.

How Act Now can help

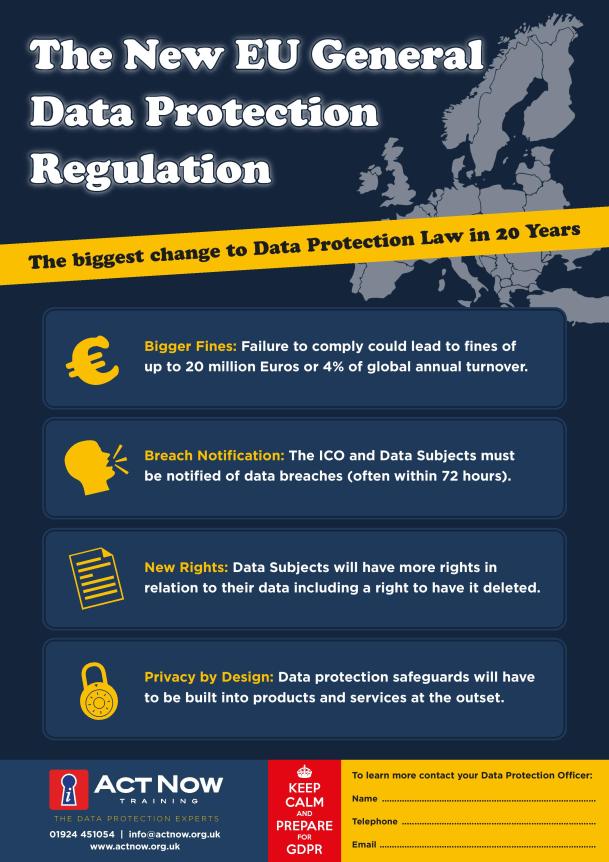
The next two years need to be spent wisely. Training and awareness (see our poster) at all levels needs to start now. We are running a series of GDPR webinars and workshops and our team of experts is available to come to your organisation to deliver customised data protection/GDPR workshops as well as to carry out health checks and audits. GDPR requires many Data Controllers to appoint a dedicated Data Protection Officer. Our GDPR Practitioner Certificate, with an emphasis on the practical skills requited to implement GDPR, is an ideal qualification for those aspiring for such positions.

And if you like our image, it, as well as some others are available as A3 Posters for the office for only £5 for three!  Take a look at the link below.

http://www.actnow.org.uk/posters

The GDPR Practitioner Certificate (GDPR.Cert) is aimed at those undertaking the role of Data Protection Officer under GDPR whether in the public or the private sector.

DP and #GDPR after #Brexit

brexit-1477615_1920

For the last six months, Data Protection experts, novices and agnostics have talked of little else but the General Data Protection Regulation, the new version of Data Protection law that will hold sway consistently across the 28 members of the European Union from the 25th May 2018.

Well, about that. 28 now becomes 27, as the United Kingdom has decided on a slim margin to vote ourselves out of the European Union, and sail off into the Atlantic. So what does this mean for the GDPR? Do we wave goodbye to the mandatory Data Protection Officer, the Right to Be Forgotten and the joys of impact assessments?

The short answer is no. The Information Commissioner has already announced that the only way forward for the UK’s creaking Data Protection legislation and its relationship with Europe is UK legislation as close to the GDPR as we can get. Every serious commentator in the Data Protection world (and all the others) are saying the same thing. The consensus is impressive but unsurprising – the redoubtable Max Schrems has proved how much creative mischief can be wrought if a country does not have a sound data protection relationship with the EU. Some of the comments coming out of the EU today make it clear how difficult it will be to achieve that relationship, so the one thing we cannot be certain of is when things will become certain.

Sooner or later, the GDPR or a close relation of it will replace the DPA in the UK. However, it is impossible to say when. Every business that offers services to EU citizens will be caught in limbo from the moment the Regulation goes live in the EU, struggling to balance the DPA in the UK and the GDPR abroad, or just succumbing to the GDPR on the basis that operating the higher GDPR standards will not cause them problems here.

In the meantime, what should organisations do? Our advice – keep your eyes peeled for the timetable for GDPR’s inception here, but look to your DP compliance now.

Consent

Whether you’re UK based or operating across the EU, the version of consent popular in the UK (implied, opt-out, buried in terms and conditions) isn’t consent. The ICO has taken enforcement action under both the DPA and the Privacy Regulations to this effect. Look everywhere that you rely on consent – you need freely given, specific and informed consent.

Fair processing

Linked to this is the issue of privacy policies and fair processing. It’s clear that the ICO does not think that long, legalistic fair processing notices are acceptable, so concentrate on communicating clearly with your customers, clients and service users.

Impact assessments

The difference between the ICO’s code on Privacy Impact Assessments and the Regulation’s requirements on impact assessments are very thin. Although the Regulation’s bold demands for Data Protection by Design (bold but not especially well explained) will only bite when we implement it, the ICO has been advocating for pro-active impact assessments in advance of new projects for a long time. We strongly advise you to look the ICO code now – it’s current good practice (and sometimes the ICO will enforce if you don’t). Moreover, it’s a dry run for the impact assessments and design principles that the GDPR will ultimately require.

Data Processors

Find every contractor and agent that your organisation does business with. Make sure there is a binding legal agreement between you and them. Like other steps we are mentioning here, this is self-preservation for the present as much for the future. If cloud computing is “your data on someone else’s computer”, then processors are “your data in the hands of someone who isn’t covered by the Data Protection Act”. Find them. Get contracts in place. Make sure they’re being followed.

Deletion

The GDPR Right to be Be Forgotten is a different beast to anything that the European courts have created under the current regime, and it is underpinned by a need to delete data from systems that process personal data. It’s well worth looking at how you might delete data and finding out where deletion / overwriting of data is difficult. When the GDPR lands, deletion will be a massive headache, but if you can’t delete now, you can’t comply with the existing Data Protection principle on retention.

Security

Every organisation needs a viable, appropriate, effective and validated security framework. Data Protection compliance under the DPA and the GDPR isn’t about incidents, it’s about effective and verified methods to prevent them, whether technical or organisational. Security isn’t everything that Data Protection is about, but there is no question that the highest penalties will still apply to poor security frameworks. The extra detail in the GDPR about security – especially what good security requires – is essential guidance and well worth implementing.

And that’s definitely not now!

BUT WHAT ABOUT….

Act Now is not predicting when the GDPR will come to the UK. Anyone who predicts confidently when it will arrive is fooling you, or themselves. The GDPR also contains a mandatory Data Protection Officer, mandatory breach notification and a whole lot else besides. It might be that the UK Government acts quickly to bring in legislation to introduce the whole package. However, while we might be confident that the GDPR is on its way, we’re not certain about when. Our advice is to work on the foundations now, and get ready to put the new GDPR structures on top when the timetable is a little clearer.

And that’s definitely not now!

Act Now continues to receive bookings for its GDPR workshops for which new dates and venues have been added. Our Data Protection Practitioner Certificate is ideal for those who want a formal qualification in this area. The syllabus is endorsed by the Centre for Information Rights based at the University of Winchester.

Nationwide breaches of DPA

clip_image002

To leave or to remain. What a difficult question and the citizens of the UK are wrestling daily with this issue under an intense barrage of claim and counter claim.

But sneaking under the radar are hundreds of breaches of Data Protection law some involving thousands or millions of data subjects. Not noticed them? If you work for a large organisation like BT or JCB your boss will have communicated to you that you should vote the way he thinks. He’s not the only one. Large companies are using the email address they hold for payroll purposes to communicate a political message to their staff. Principle 1 says

“Personal data shall be processed fairly and lawfully (and according to a condition from Schedule 2 and/or 3)”

They could look for a justification in Schedule 2 but they’d be better looking in Schedule 3 as political data is sensitive. So consent turns into the slightly more difficult informed consent but which employee ever consents that his data will be used to tell him which way to vote and which employer ever thought he’d need to help his employees with voting. Old faithful Schedule 2 (6) allows

“The processing is necessary for the purposes of legitimate interests pursued by the data controller or by the third party or parties to whom the data are disclosed, except where the processing is unwarranted in any particular case by reason of prejudice to the rights and freedoms or legitimate interests of the data subject.”

Which data subject would accept that political lobbying is warranted with his payroll data and who would ever say that voting recommendations were a legitimate interest of your boss. So all schedules are out of the window. So they can’t do it lawfully and/or fairly. Principle 1 breached.

Principle 2 says

“Personal data shall be obtained only for one or more specified and lawful purposes, and shall not be further processed in any manner incompatible with that purpose or those purposes.”

Specified means in fair processing and notification sent to Commissioner. So if an organisation hasn’t said to its employees that it will use their personal data for pushing a political end they can’t do it. Principle 2 breached.

It may be that these companies are stretching the definition of personnel & payroll to include ‘what might happen to your pay if we left the EU’ but it’s quite a long stretch. It may end up with someone in authority making a judgement one day. But time is short and it’s unlikely anyone will be interested after the polling stations close.

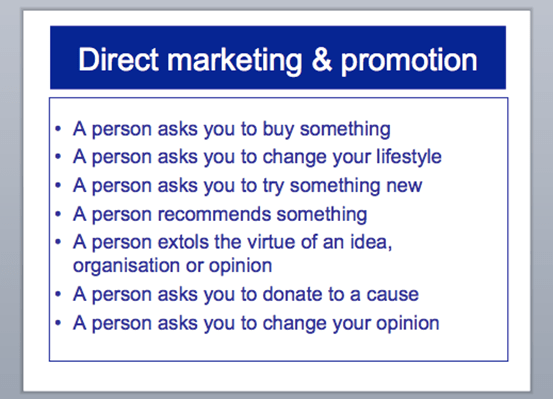
And these employers trying to influence people’s opinions or beliefs drops into the ICO definition of direct marketing.

clip_image004

Quite a few of these fit neatly with the leave/remain issue. If employers are doing it by electronic means then PECR applies. You could argue that a corporate email address isn’t personal data but there are plenty who will argue that it is. (But PECR’s only concerned with subscribers isn’t it?)

Further afield European businessmen are trying to help us make up our mind as well.

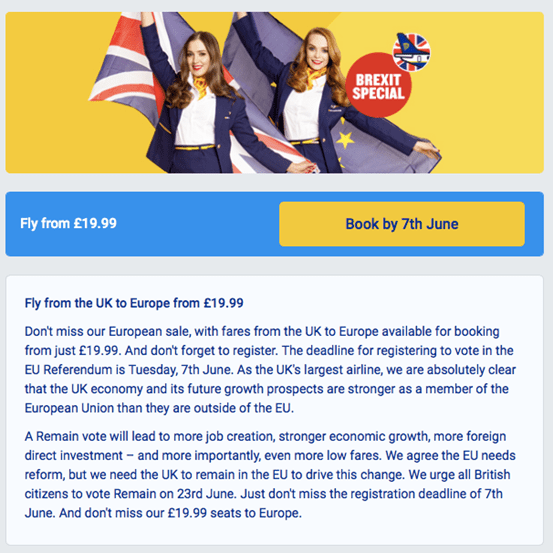
An email sent to a few million people recently (all the people who’ve ever flown with Ryanair) was brazenly labelled Brexit Special. Even with a public service announcement thrown in it clearly used email addresses collected for administration of air travel to influence voting intentions.

clip_image006

So there’s a possibility that millions of data subjects are having their rights infringed and Breaches of the DPA are legion. Captains of industry could argue that it’s their personal view to leave/remain not the corporate body that holds the payroll data but that just opens up another can of worms doesn’t it. We may get as far as a criminal offence of procuring or unauthorised obtaining if the boss uses the company data for a personal purpose.

At least it’s only a few breaches of the Data Protection Act. It could be worse – they could be lying to us.

It’ll all be forgotten on Friday morning. (Until the next referendum)

Act Now can help you prepare for the Regulation. Our one day GDPR workshops are ideal for those wanting to get a headstart in their preparations.

To Brexit or not to Brexit…

canstockphoto35750834


That is the question on everyone’s lips right now. With the EU referendum looming, the next big question is, How will the GDPR affect us should we decide to leave the EU? The majority opinion is that we will be definitely affected in some way or other by the regulation and most likely will have to adopt all of it, maybe in a slower timeframe… But there’s no escaping it!

There’s three likely outcomes should we leave the EU…

  1. We remain in the European free trade association or Economic area (EEA) of the EU similar to Norway in which case we would then be subjected to GDPR, in order to trade with the EU
  1. We leave all trade agreements and become similar to the USA – a ‘safe third country’, in which case we would have to have a suitable level of DP Regulation which for all intents and purposes will be the GDPR
  1. We completely go solo like Geri Halliwell, Robbie Williams, Zayn Malik…okay i’ll stop. Even in this scenario, we would have to make our own singles, do our own world tours… sorry, i mean have our own equivalent GDPR, or update our existing one and where better to find one? (I can sense a Blue Peter moment coming on…)

So in short… and forgive me for my Hunger Games level of enthusiasm of being selected in the games, but GDPR is coming one way or the another…The Real Question is… Are You Ready?

Let the Games Begin!


Act Now can Help you prepare for the regulation. We have full day courses on the regulation as well as courses available online. Please visit our website here to find out more.


25th May 2018: D-day For Data Protection (GDPR)

canstockphoto30465718

Following its formal adoption by the European Parliament in April, the General Data Protection Regulation (GDPR) was published on 4th May 2016 in the Official Journal. This means that it will be directly applicable throughout the EU (without the need for implementing legislation) from 25th May 2018.

Data Controllers now have two years to prepare for the biggest change to the EU data protection regime in 20 years.  With some breaches of the Regulation carrying fines of up to 4% of global annual turnover or 20 million Euros, everyone has to take Data Protection seriously.

 All Data Protection practitioners and lawyers need to read the Regulation and consider its impact on their organisation and clients. Act Now has a series of blog posts as well as a dedicated GDPR section on its website with articles on the different aspects of the Regulation.

Training and awareness at all levels needs to start now. We are running a series of GDPR webinars and workshops. Five out of eight of the next GDPR workshops are fully booked. We have also started running workshops on specific aspects of the Regulation e.g. Information Risk and Security.

Our team of experts is available to come to your organisation to deliver customised data protection/GDPR workshops as well as to carry out health checks and audits.

If you are looking for an up to date DP qualification with a focus on GDPR, have a look at our Data Protection Practitioner Certificate.

The next two years need to be spent wisely. Act Now can help you prepare for the Regulation in the most cost effective manner whilst also ensuring you and your organisation are fully prepared.

Let the Fun Begin! New EU Data General Protection Regulation #GDPR is Adopted

eu falg.jpg

After four years of negotiation, the new EU General Data Protection Regulation (GDPR) has today been formally adopted by the European Parliament. The Regulation will soon be available in all the official EU languages.

The Regulation will take effect twenty days from its post-vote publication in the Official Journal (May 2018) giving Data Controllers two years to prepare for the biggest change to the EU data protection regime in 20 years.

The Regulation will apply to any entity offering goods or services (regardless of payment being taken) and any entity monitoring the behaviours of citizens residing within the EU. Companies are now directly responsible for DP compliance wherever they are based (and not just their EU based offices) as long as they are processing EU citizens’ personal data.

For some breaches of the Regulation (e.g. failing to comply with Data Subjects’ rights or the conditions for processing) Data Controllers can receive a fine of up to 4% of global annual turnover for the preceding year (for undertakings) or 20 million Euros. For other breaches (e.g. failing to keep records or complying with security obligations) the fine can be up to 10 million Euros or 2% of global annual turnover (for undertakings).

The Regulation replaces the previous EU Data Protection Directive (95/46/EC), upon which the UK’s Data Protection Act 1998 (DPA) is based, without the need for further national legislation. It does though allow for substantial national derogations in a number of important areas, so in addition to amending or repealing their existing legislation and guidance, the Government and the Information Commissioner’s Office(ICO) will be working to finalise their positions on key issues such as exemptions, workplace privacy, healthcare services and biomedical research.

The ICO has set up a new GDPR microsite and published a 12 step guide to preparing for the Regulation. Read the Assistant Information Commissioner’s blog here about what more they are planning.

The Regulation is accompanied by the EU Policing and Criminal Justice Data Protection Directive which contains new rules for Data Protection when applied to crime and justice, but which can be implemented by each Member State through its own laws with greater flexibility.

 All Data Protection practitioners and lawyers need to read the Regulation and consider its impact on their organisation and clients. The good people at Covington & Burling LLP have published an automated comparison here to allow readers to see how the Regulation has changed from its previous version.

Training and awareness at all levels needs to start now. Here is a nice video to get you started.

Act Now has a dedicated GDPR section on its website containing articles as well as details of our GDPR webinars and workshops. If you are looking for an up to date DP qualification with a focus on GDPR, have a look at our Data Protection Practitioner Certificate.